Vates VMS Warns of Actively Exploited Xen Orchestra Authentication Bypass
Vates VMS is alerting customers to a critical authentication bypass in Xen Orchestra that the French software company says is being exploited in the wild. The flaw, tracked as VSA-2026-062, has no...
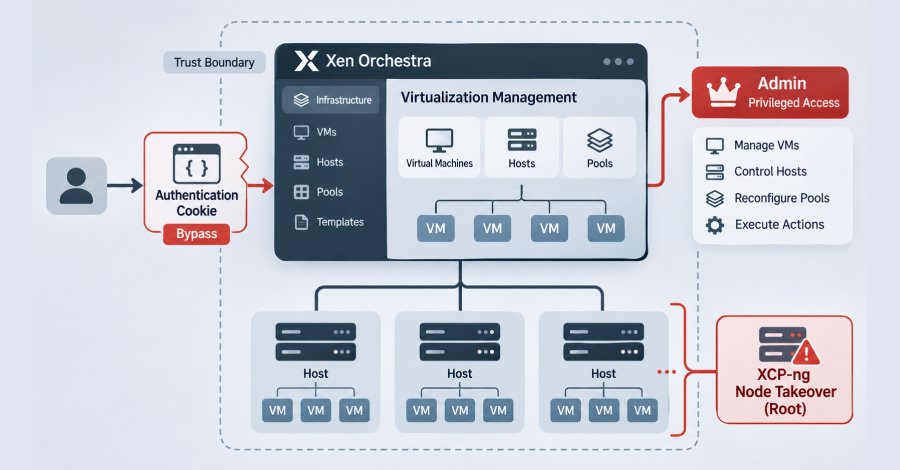
Vates VMS is alerting customers to a critical authentication bypass in Xen Orchestra that the French software company says is being exploited in the wild. The flaw, tracked as VSA-2026-062, has no CVE identifier yet.
According to Vates VMS, REST cookie parsing converts authenticationToken=j:%7B%7D into {}, and REST authentication hands that object to the XO token provider without requiring a string. The token collection then treats {} as an unfiltered lookup and returns its first token, letting the provider authenticate as that token's owner if it has not expired. The authenticated /rest/v0/users/me/authentication_tokens route then returns reusable login token IDs.
In practice, an attacker can send a specially crafted cookie to skip authentication and act with Admin privileges, leading to arbitrary code execution on managed pools and a full XCP-ng node takeover as root.
Vates VMS says it has observed exploitation from 91.211.251[.]112:8001, flagged on VirusTotal as a RedLine Stealer command-and-control server, and from the TOR domain ustar3rqxgnskzgnwkgpofgtvxevm6cx3lxdbwt4mndtveqyaohid[.]onion:3333. It is unclear when the activity began or whether the flaw was used as a zero-day.
Indicators of compromise include HTTP requests containing authenticationToken=j:%7B%7D or authenticationToken=j:{}, a running virtual machine named pivot2, virtual machines configured with the hvm_serial: file parameter, and suspicious files named /etc/cron.d/zz-ustar2, /etc/cron.d/zz-ustar, /.ustar5 and /.ustar6.
The issue is fixed in Xen Orchestra 6.9.1 and 6.10.0 for the stable and latest channels, and in xo-server versions 5.211.2 and 5.213.1. Where patching is not immediately possible, Vates VMS advises keeping Xen Orchestra instances off the internet, blocking the malicious IP address and domain, blocking the empty token in a web application firewall or reverse proxy, and rotating all passwords and secrets if indicators of compromise are found.
Filip Magic (@mad31k) and Christoffer Olsen of TDC NET Security have been credited with discovering and reporting the flaw.
Source: The Hackers News
Ready to Modernize Your Business?
Get your AI automation roadmap in minutes, not months.
Analyze Your Workflows →