Researchers Use Claude to Move a Pre-Auth RCE Attack Between Two PLC Models
Forescout Research's Vedere Labs says it used Anthropic's Claude to transfer a working pre-authentication remote code execution (RCE) exploit from one WAGO programmable logic controller (PLC) to...
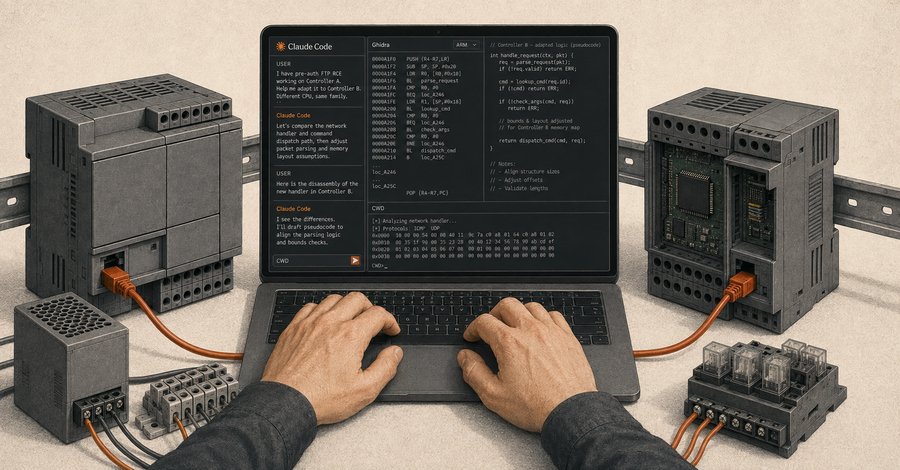
Forescout Research's Vedere Labs says it used Anthropic's Claude to transfer a working pre-authentication remote code execution (RCE) exploit from one WAGO programmable logic controller (PLC) to another, successfully running attacker-supplied ARM shellcode on live hardware.
The exploit targets CVE-2021-31886, a stack-based buffer overflow in the Nucleus FTP server's handling of the USER command. The vulnerability carries a Siemens-assigned CVSS score of 9.8 and is reachable before authentication over TCP port 21. CERT@VDE says no updates are available for the affected WAGO controllers and advises owners to disable or block FTP on port 21, enforce network segmentation, and monitor for anomalies.
The porting effort required continuous researcher guidance. The final stage of RCE development consumed $535.74 in API usage over an 8-hour-32-minute session. A later attempt to extend the exploit into a command-and-control implant wrote to a flash-mapped memory region, permanently bricking the PLC. Forescout notes that a skilled researcher might have completed the initial RCE port faster and cheaper without AI, while also keeping the device functional.
Vedere Labs had previously built a working exploit for the WAGO 750-852 and ported it to a 750-831 running firmware V01.04.16. Researchers supplied the existing exploit, a firmware binary, and a physical 750-831 as the live target. Each stage ran as interactive sessions between a researcher and Claude Code, which had access to a terminal, the reverse-engineering tool Ghidra, and the PLC.
Work began on Claude Sonnet 4.6 and moved to Claude Opus 4.6 after early attempts stalled. Normal FTP processing on the 750-831 zeroed 256 bytes at the attacker-controlled buffer, overwriting injected shellcode before it could run. Claude adapted the USER and QUIT sequence used on the 750-852 into a USER and CWD sequence. By omitting the CRLF terminator, the relevant processing path did not complete as usual, allowing the buffer to survive long enough for payload execution.
Once code execution was achieved, the model moved from no-operation shellcode to two functional payloads in 12 minutes. One sent ICMP echo requests to an attacker-controlled system; the other sent a UDP packet containing the string PWNED. The exploit runs in the Ethernet receive callback context, and the demonstrated capability stops at sending network packets.
Forescout said Claude also flagged a potential bug in the FTP command extraction loop during the first session, distinct from CVE-2021-31886. Manual review suggested this could be a separate, previously unidentified vulnerability. The team set it aside for further investigation, and it carries no CVE identifier.
A GitHub repository search for CVE-2021-31886, run by The Hacker News on September 1, returned no results. The flaw is absent from Exploit-DB and Packet Storm. That search indexes repository names and descriptions rather than file contents.
Forescout warns that the more immediate risk is not an AI agent independently deciding to attack a controller, but an authorized agent taking the wrong action on a physical system where failure has real operational consequences.
The CERT@VDE advisory lists multiple WAGO devices as vulnerable, including the 750-829, 750-831/000-00x, 750-852, 750-880/0xx-xxx, 750-881, 750-882, 750-885/0xx-xxx, 750-889, 750-331, and 750-352/xxx-xxx. The advisory notes these devices run Nucleus V1 RTOS and no updates are available. Two models, the 750-882 and 750-885/0xx-xxx, are absent from both the mitigation section and remediation table, leaving their fix status unstated.
Siemens, which maintains Nucleus, states no remediation is planned for Nucleus NET across all versions. Nucleus ReadyStart V3 releases from V2013.08.1 onward already fix CVE-2021-31886. The flaw was one of 13 disclosed in November 2021 as NUCLEUS:13 by Forescout and Medigate.
The research follows a joint advisory issued August 19 by the NSA, CISA, FBI, Department of Energy, and Environmental Protection Agency warning of an active threat to internet-exposed Siemens S7 Series PLCs from AI-generated exploitation scripts. The agencies assess the activity is likely for persistent reconnaissance and capability development and have stopped short of attribution. Separately, the FBI and EPA reported attacks on water utilities in at least seven states since July 27, with actors changing IP addresses and passwords on internet-facing Rockwell Automation MicroLogix controllers in attacks needing no exploit. The agencies said AI-generated exploitation scripts dramatically reduce the technical expertise and time required to develop working ICS exploits.
Source: The Hackers News
Ready to Modernize Your Business?
Get your AI automation roadmap in minutes, not months.
Analyze Your Workflows →