Researchers Say AI-Assisted Chain Compromised OpenAI Staff Accounts Through Forum Bug
A security team says it used an AI model to string together two software flaws and gain access to OpenAI employees' ChatGPT and Codex accounts, then reach an internal OpenAI code repository. The...
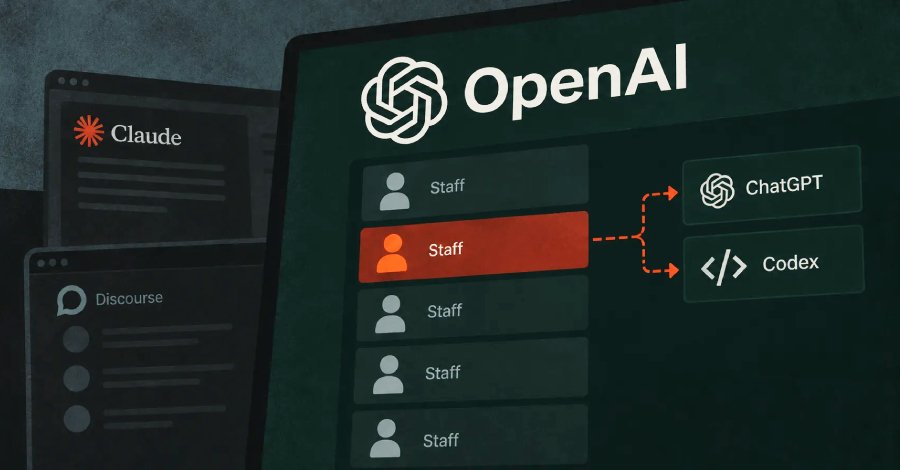
A security team says it used an AI model to string together two software flaws and gain access to OpenAI employees' ChatGPT and Codex accounts, then reach an internal OpenAI code repository. The work was conducted as controlled research, not a real-world intrusion.
According to the researchers, the chain started with a bug in the software running OpenAI's public help forum and then moved through a weakness in OpenAI's login system. They reported the flaws to OpenAI, demonstrated the access with a harmless pull request, and stopped. OpenAI confirmed a fix and later paid a bounty, though it has not publicly detailed the login flaw.
The researchers say the forum's image-handling component was the entry point, and that the shared sign-on used by staff was what allowed forum access to become account access. They also say the same access could in theory have extended to connected tools, but that wider reach was not used.
The team has described broader findings across other companies, but those claims have not been uniformly confirmed. There is no indication the flaws were used against anyone in the real world.
Source: The Hackers News
Ready to Modernize Your Business?
Get your AI automation roadmap in minutes, not months.
Analyze Your Workflows →