Paperclip Security Flaws Could Let Attackers Run Commands on Servers and Developer Machines
Two security vulnerabilities in Paperclip, an open-source control plane for AI agent teams, could allow attackers to execute commands on a network server or a developer's computer. Both attack...
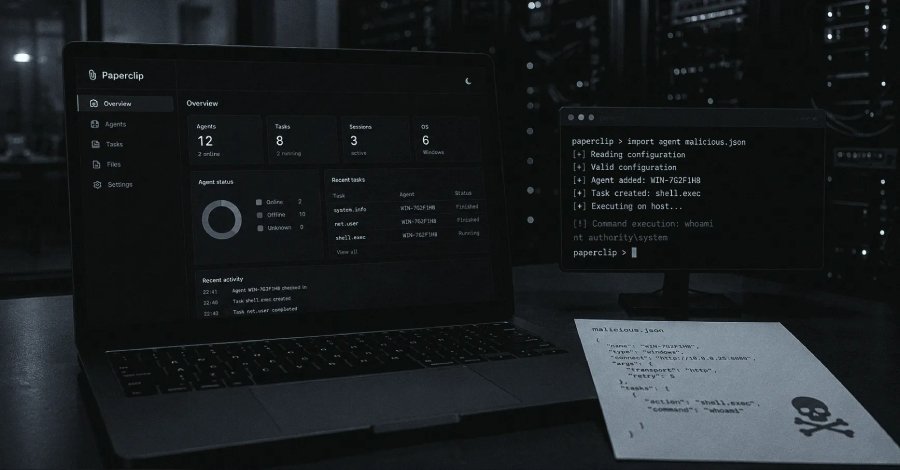
Two security vulnerabilities in Paperclip, an open-source control plane for AI agent teams, could allow attackers to execute commands on a network server or a developer's computer. Both attack paths involve importing a malicious agent and then starting it. A third flaw could expose sensitive data and control-plane details through API routes that lacked proper access checks.
The most severe issue, tracked as CVE-2026-41679 with a perfect CVSS score of 10.0, targets network-accessible deployments using authenticated mode with the default registration setup. It requires no pre-existing account or victim interaction. The second critical path, tracked as GHSA-x8hx-rhr2-9rf7 with a score of 9.6, needs a user to open an attacker-controlled page while Paperclip runs in its default local_trusted mode.
The server-side attack begins with Paperclip's open-signup flow. An attacker can register without an invitation or verified email, then create and approve their own CLI challenge, gaining a durable board API credential. That credential, though not meant for top-level company creation, could be used through the import route to define a new company with an agent that runs a command. Once the attacker starts the agent, Paperclip executes the command with the server's operating-system privileges.
The localhost attack uses DNS rebinding. An attacker-controlled hostname alternates between the attacker's server and 127.0.0.1. After the browser loads JavaScript from the attacker, later requests to the same hostname reach the local Paperclip service, which treats them as same-origin. Because local mode grants administrator authority to all requests, the attacker's command runs with the developer's privileges - no token or credential needed.
The third advisory, GHSA-xfqj-r5qw-8g4j with a score of 8.3, covers API routes in authenticated mode that failed to reject unauthenticated or cross-company requests. Some routes exposed skill documentation, health details, or issue data tied to heartbeat-run identifiers.
Paperclip addressed the issues in the source tagged as v2026.416.0, which includes import-authorization fixes and hostname validation. Rapid7 published a Metasploit module for CVE-2026-41679 in June 2026, and NVD's enrichment classifies exploitation as proof-of-concept. As of August 5, 2026, no exploitation in the wild had been reported, and the flaw was not in CISA's KEV catalog. Operators should update to v2026.416.0 or later and review their registration and deployment exposure settings.
Oasis Security, which provided the analysis, stressed that agent configuration must be treated as executable input. The records for patched versions are inconsistent - the GitHub release uses v2026.416.0 while internal manifests report 0.3.1 - so the safest upgrade point is v2026.416.0 or later.
Source: The Hackers News
Ready to Modernize Your Business?
Get your AI automation roadmap in minutes, not months.
Analyze Your Workflows →