IBM Warns of Critical Langflow Authentication and Code Execution Flaws
Two critical vulnerabilities in Langflow, an open-source tool for building AI agents and workflows, could allow remote attackers without an account to bypass authentication or execute arbitrary...
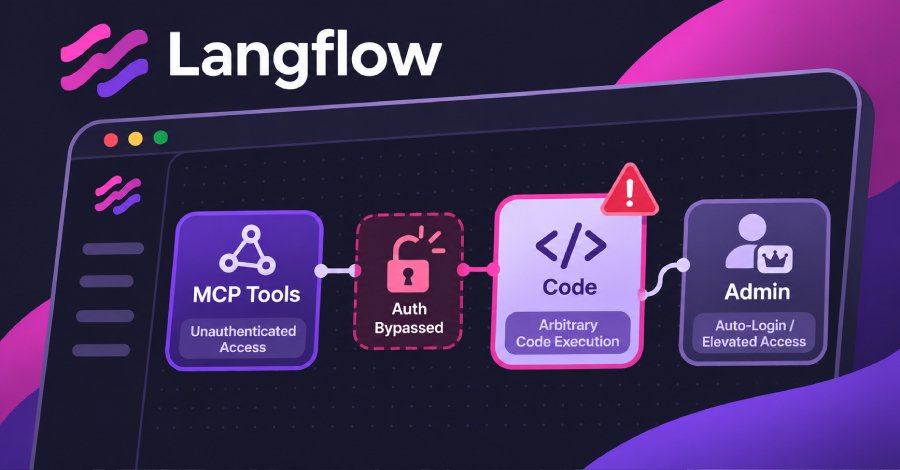
Two critical vulnerabilities in Langflow, an open-source tool for building AI agents and workflows, could allow remote attackers without an account to bypass authentication or execute arbitrary code, IBM reported last week. Every release from 1.0.0 through 1.12.8 is affected, and the only fix is version 1.13.0.
The flaws, tracked as CVE-2026-93680 and CVE-2026-110186, both carry a CVSS score of 9.8 and require no account to exploit. One is described by IBM as unauthenticated remote code execution exploitable through Model Context Protocol tool enumeration. A Metasploit Framework module already cites the authentication bypass, though it only lists tools on a server and does not run code.
Neither flaw appears in CISA's Known Exploited Vulnerabilities catalog as of its October 30 update. IBM's bulletin, first published October 28, also details two lower-severity flaws requiring a low-privileged account: one rated 8.8 that could let the Agentic Assistant run operating system commands, and one rated 6.5 involving insufficiently protected credentials.
Langflow 1.13.0 was released October 22 and disables automatic login by default. IBM offers no workaround for servers that cannot upgrade. The bulletin does not say whether servers with automatic login turned off are vulnerable. IBM also published CVE records for 29 other Langflow flaws on October 29, naming versions 1.12.4 and 1.12.5 as their fixes.
Source: The Hackers News
Ready to Modernize Your Business?
Get your AI automation roadmap in minutes, not months.
Analyze Your Workflows →