FoxIO Finds QPACK Flaws That Can Crash HTTP/3 Servers, With Memory Amplification Up to 4,000-Fold
Security firm FoxIO has disclosed flaws in QPACK, the header compression scheme used by HTTP/3, that let an unauthenticated remote attacker crash many HTTP/3 web servers with a single connection....
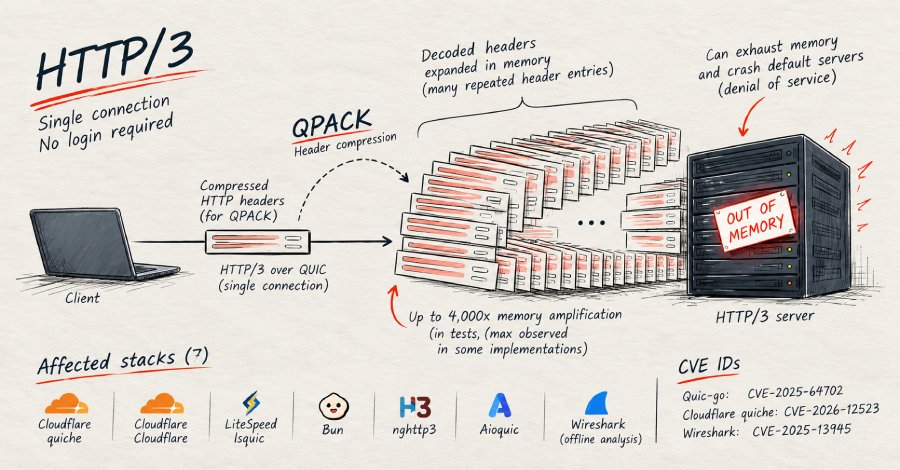
Security firm FoxIO has disclosed flaws in QPACK, the header compression scheme used by HTTP/3, that let an unauthenticated remote attacker crash many HTTP/3 web servers with a single connection. FoxIO released working proof-of-concept code alongside the findings.
The attack works by sending a small batch of compressed HTTP headers that expands into a far larger set in memory. A server is meant to cap header size after unpacking, but the affected stacks cap only the compressed data on the wire, or apply the limit too late, so one request can balloon into hundreds of thousands of header entries held in memory. The flaws enable denial-of-service only; there is no evidence of data theft or code execution and no public reports of attacks in the wild.
FoxIO found the same class of flaw in seven of ten HTTP/3 stacks it tested. Fixes are available for quic-go (0.57.0, CVE-2025-64702), Cloudflare quiche (0.29.3, CVE-2026-12523), lsquic (4.9.0, no CVE) and Wireshark (4.6.2 / 4.4.12, CVE-2025-13945). Bun, the h3 Rust library and aioquic remained unpatched at disclosure.
The reach is broad because these stacks underpin common software: quic-go powers Caddy, Traefik and cloudflared; lsquic is LiteSpeed's library, used in LiteSpeed Web Server and OpenLiteSpeed; and Bun's HTTP/3 server runs on lsquic. No account or special access is needed, and because HTTP/3 runs over UDP, requests arrive before much usual filtering applies.
Amplification varies by stack. In FoxIO's tests, a 1 MB compressed batch on quic-go unpacked into about 160,000 header fields, leaving roughly 15 MB held in the request - about 17 times the bytes sent; quic-go's advisory cites around 50 times. A second method stores one roughly 4 KB header entry and references it thousands of times with one-byte pointers, yielding about 4,000-fold expansion on Bun and 600 to 1,800 times on lsquic.
Bun carries the worst case. Its experimental HTTP/3 server uses lsquic but replaces the header-memory cap with its own code, which checks each header but never the running total. FoxIO found that once unpacked headers pass 2 GB, a size counter overflows to zero and the server enters a loop it never leaves. A single stream carrying about 516 KB on the wire leaves the server stuck at 100 percent CPU with no recovery, blocking new requests.
Wireshark's issue is different: it crashes the HTTP/3 dissector when Wireshark decrypts traffic using a key-log file or opens a capture holding decryption secrets. It is not a remotely reachable server flaw, and Wireshark said it is unaware of any exploits.
Operators should upgrade to the fixed releases. For unpatched stacks, FoxIO advises not exposing a Bun HTTP/3 server, disabling HTTP/3 in mitmproxy with --set http3=false, and setting max_field_section_size for the h3 Rust library. The lsquic fix, released July 16, 2026, caps unpacked header sets per stream at one by default. FoxIO said the work began after Gal Bar Nahum's research into MadeYouReset, an HTTP/2 denial-of-service technique, which asked whether HTTP/3's header compression had a similar weakness.
Source: The Hackers News
Ready to Modernize Your Business?
Get your AI automation roadmap in minutes, not months.
Analyze Your Workflows →